- Entra security
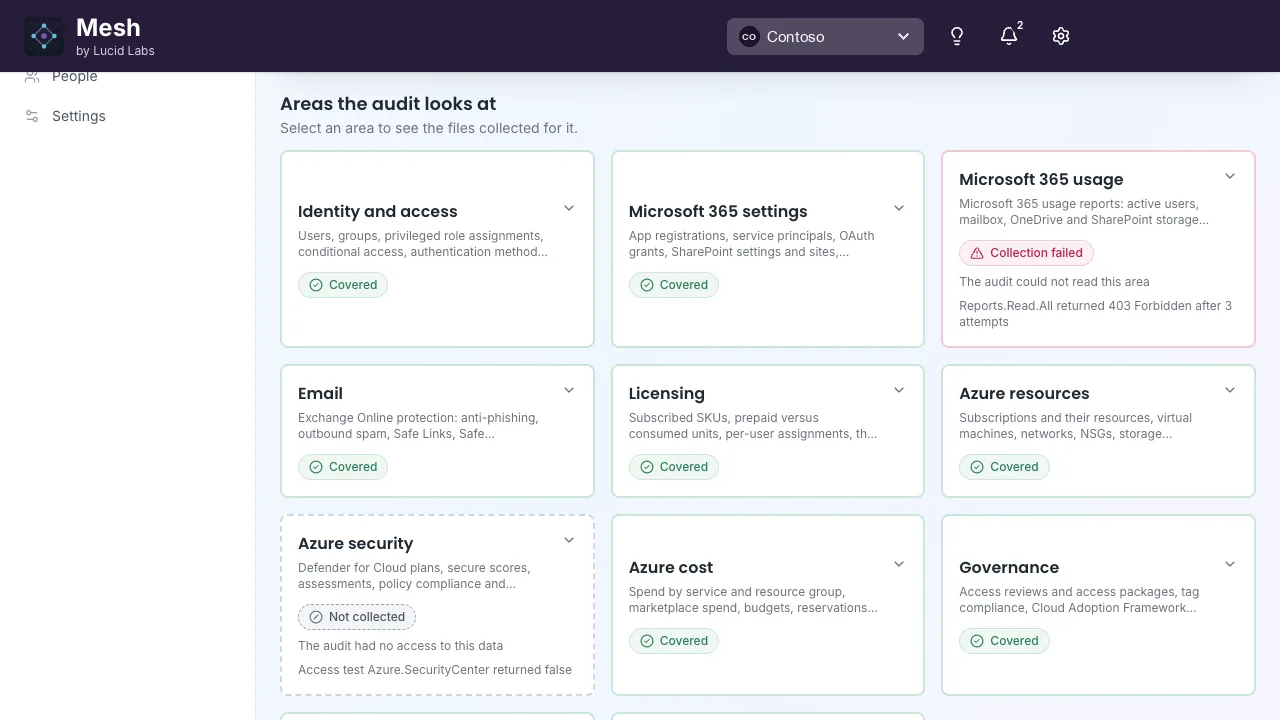
- Users, groups, privileged roles, Conditional Access, authentication methods, cross-tenant access and audit logs, plus the Maester baseline tests.
- Microsoft 365 configuration
- App registrations and consent grants, SharePoint settings and oversharing, Intune policies and devices, Microsoft Places and Defender alerts.
- Microsoft 365 adoption
- Active users, mailbox, OneDrive and SharePoint storage, and Teams and email activity over 30 and 90 days.
- Email security
- Anti-phishing, outbound spam, Safe Links, Safe Attachments, transport rules, connectors, domains and mailbox forwarding.
- Data protection
- Microsoft Purview data loss prevention policies and the locations they enforce on, including Microsoft 365 Copilot, plus sensitivity labels, label publishing, default and mandatory labelling, and auto-labelling.
- Agents
- The Copilot agent estate from the Agent 365 catalogue: unmanaged and tenant-wide agents, pending agent requests and blocked agents still deployed, plus Conditional Access coverage of agent identities, open agent risk detections and whether DLP and Insider Risk policies reach agents.
- Licensing
- Subscribed SKUs, licences bought against licences assigned, per-user assignments and what can be reclaimed.
- Azure resources
- Subscriptions and their resources: virtual machines, networks, storage accounts, key vaults, SQL and App Service.
- Azure security
- Defender for Cloud plans and secure score, policy compliance, CIS and Azure hardening checks, and Azure role assignments.
- Azure Cost Management
- Spend by service and resource group, marketplace spend, budgets, reservations, Advisor cost recommendations and the cost-optimisation analysis.
- Governance
- Access reviews and access packages, tag compliance and Cloud Adoption Framework alignment.
- Fabric and Power BI
- Workspaces, capacities, semantic models, reports, tenant settings and publish-to-web exposure.
- Power Platform
- Who administers Power Platform and Dynamics 365, who holds their licences, service principals, Copilot Studio agent identities and consents.
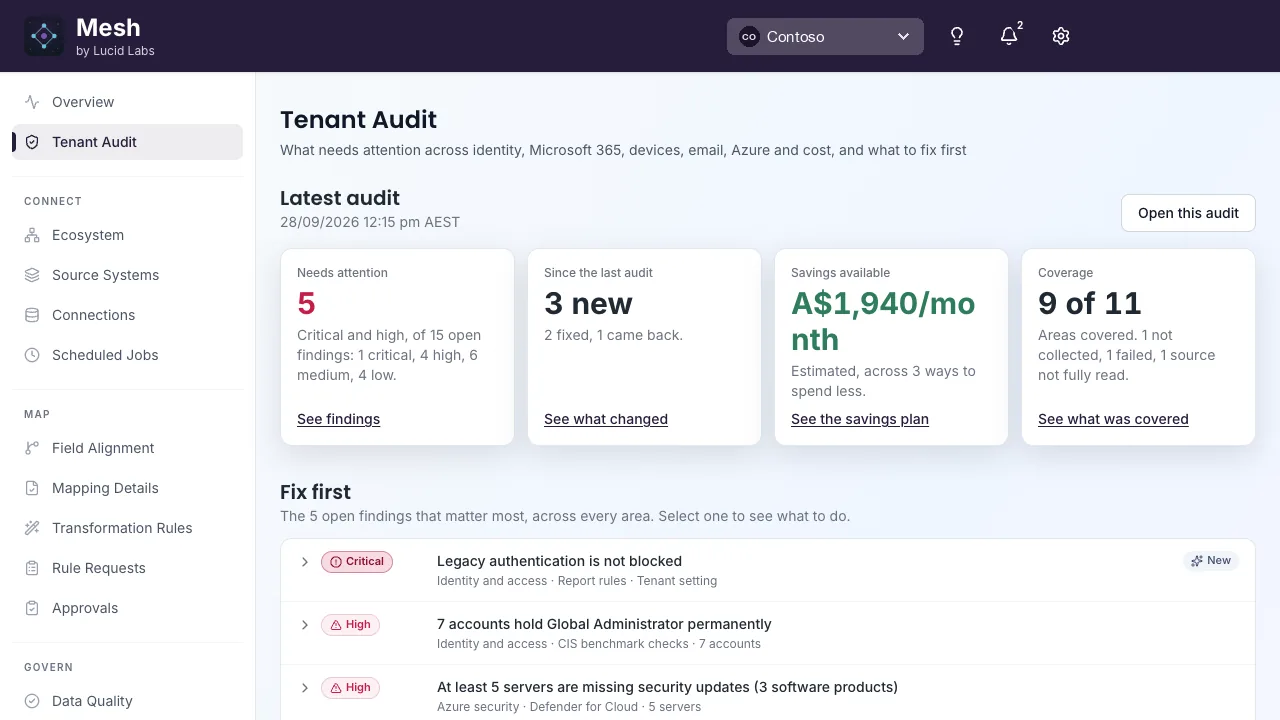
Most areas need only the audit app’s consent. The Azure areas also need read roles on your subscriptions: Reader, Security Reader, Monitoring Reader and Cost Management Reader. Email needs an Exchange permission and the View-Only Organization Management role group, and access reviews need Microsoft Entra ID P2 or ID Governance. An area the audit could not read is marked not collected.